
52 lines
3.6 KiB
XML
52 lines
3.6 KiB
XML
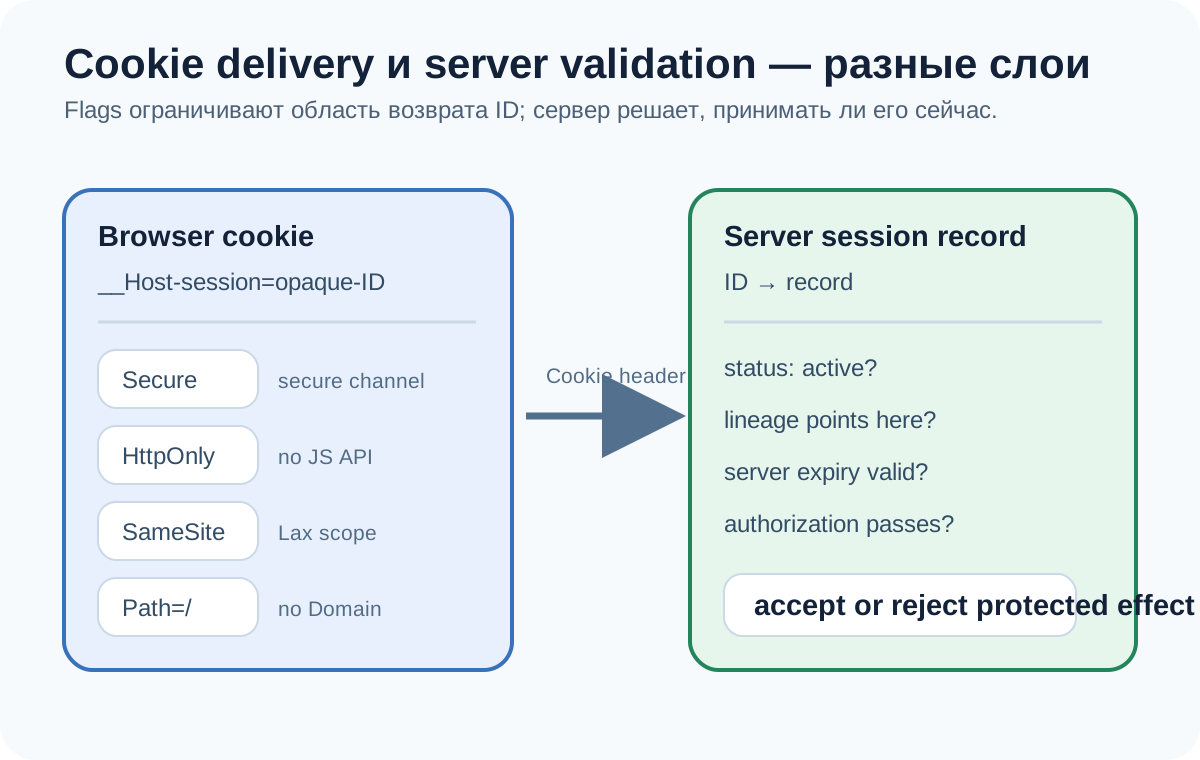


<svg xmlns="http://www.w3.org/2000/svg" viewBox="0 0 1200 760" role="img" aria-labelledby="sessions-auth-2023-cookie-contract-title sessions-auth-2023-cookie-contract-desc">
|
||
<title id="sessions-auth-2023-cookie-contract-title">Контракт cookie и серверной сессии</title>
|
||
<desc id="sessions-auth-2023-cookie-contract-desc">Cookie с именем __Host-session несёт непрозрачный ID. Secure, HttpOnly, SameSite, Path и отсутствие Domain ограничивают доставку в браузере. Сервер отдельно проверяет status, current lineage и expiry.</desc>
|
||
<style>
|
||
.bg { fill: #f7fafc; }
|
||
.title { fill: #132238; font: 700 42px Arial, sans-serif; }
|
||
.sub { fill: #4b5f76; font: 500 24px Arial, sans-serif; }
|
||
.browser { fill: #e8f0fe; stroke: #3972b8; stroke-width: 4; }
|
||
.server { fill: #e6f6ec; stroke: #24855d; stroke-width: 4; }
|
||
.pill { fill: #ffffff; stroke: #cbd8e6; stroke-width: 2; }
|
||
.head { fill: #132238; font: 700 29px Arial, sans-serif; }
|
||
.body { fill: #334c65; font: 500 24px Arial, sans-serif; }
|
||
.small { fill: #526c85; font: 500 21px Arial, sans-serif; }
|
||
.arrow { stroke: #53718e; stroke-width: 7; fill: none; marker-end: url(#sessions-auth-2023-cookie-contract-arrow); }
|
||
.divider { stroke: #cbd8e6; stroke-width: 3; }
|
||
</style>
|
||
<defs>
|
||
<marker id="sessions-auth-2023-cookie-contract-arrow" markerWidth="12" markerHeight="12" refX="10" refY="6" orient="auto"><path d="M0,0 L12,6 L0,12 Z" fill="#53718e"/></marker>
|
||
</defs>
|
||
<rect class="bg" width="1200" height="760" rx="34"/>
|
||
<text class="title" x="64" y="78">Cookie delivery и server validation — разные слои</text>
|
||
<text class="sub" x="64" y="118">Flags ограничивают область возврата ID; сервер решает, принимать ли его сейчас.</text>
|
||
<rect class="browser" x="64" y="190" width="448" height="480" rx="28"/>
|
||
<text class="head" x="98" y="246">Browser cookie</text>
|
||
<text class="body" x="98" y="290">__Host-session=opaque-ID</text>
|
||
<line class="divider" x1="98" y1="322" x2="476" y2="322"/>
|
||
<rect class="pill" x="98" y="350" width="160" height="58" rx="18"/>
|
||
<text class="body" x="122" y="388">Secure</text>
|
||
<text class="small" x="278" y="388">secure channel</text>
|
||
<rect class="pill" x="98" y="426" width="160" height="58" rx="18"/>
|
||
<text class="body" x="122" y="464">HttpOnly</text>
|
||
<text class="small" x="278" y="464">no JS API</text>
|
||
<rect class="pill" x="98" y="502" width="160" height="58" rx="18"/>
|
||
<text class="body" x="122" y="540">SameSite</text>
|
||
<text class="small" x="278" y="540">Lax scope</text>
|
||
<rect class="pill" x="98" y="578" width="160" height="58" rx="18"/>
|
||
<text class="body" x="122" y="616">Path=/</text>
|
||
<text class="small" x="278" y="616">no Domain</text>
|
||
<path class="arrow" d="M526 416 H672"/>
|
||
<text class="small" x="546" y="383">Cookie header carries ID</text>
|
||
<rect class="server" x="690" y="190" width="446" height="480" rx="28"/>
|
||
<text class="head" x="724" y="246">Server session record</text>
|
||
<text class="body" x="724" y="290">ID → record</text>
|
||
<line class="divider" x1="724" y1="322" x2="1102" y2="322"/>
|
||
<text class="body" x="724" y="376">status: active?</text>
|
||
<text class="body" x="724" y="428">lineage points here?</text>
|
||
<text class="body" x="724" y="480">server expiry valid?</text>
|
||
<text class="body" x="724" y="532">authorization passes?</text>
|
||
<rect class="pill" x="724" y="574" width="352" height="62" rx="18"/>
|
||
<text class="head" x="754" y="615">accept or reject protected effect</text>
|
||
</svg>
|